Book a call

Research

Evidence anyone can check

We study the three moments where an agent's trustworthiness can be tested, and map the rest of the field to decide where to look next. Every project and paper ships with its code and data.

Projects

Working tools, testbeds and methods. Filter by program.

All 7 projects

Proof-Carrying Messages

Released

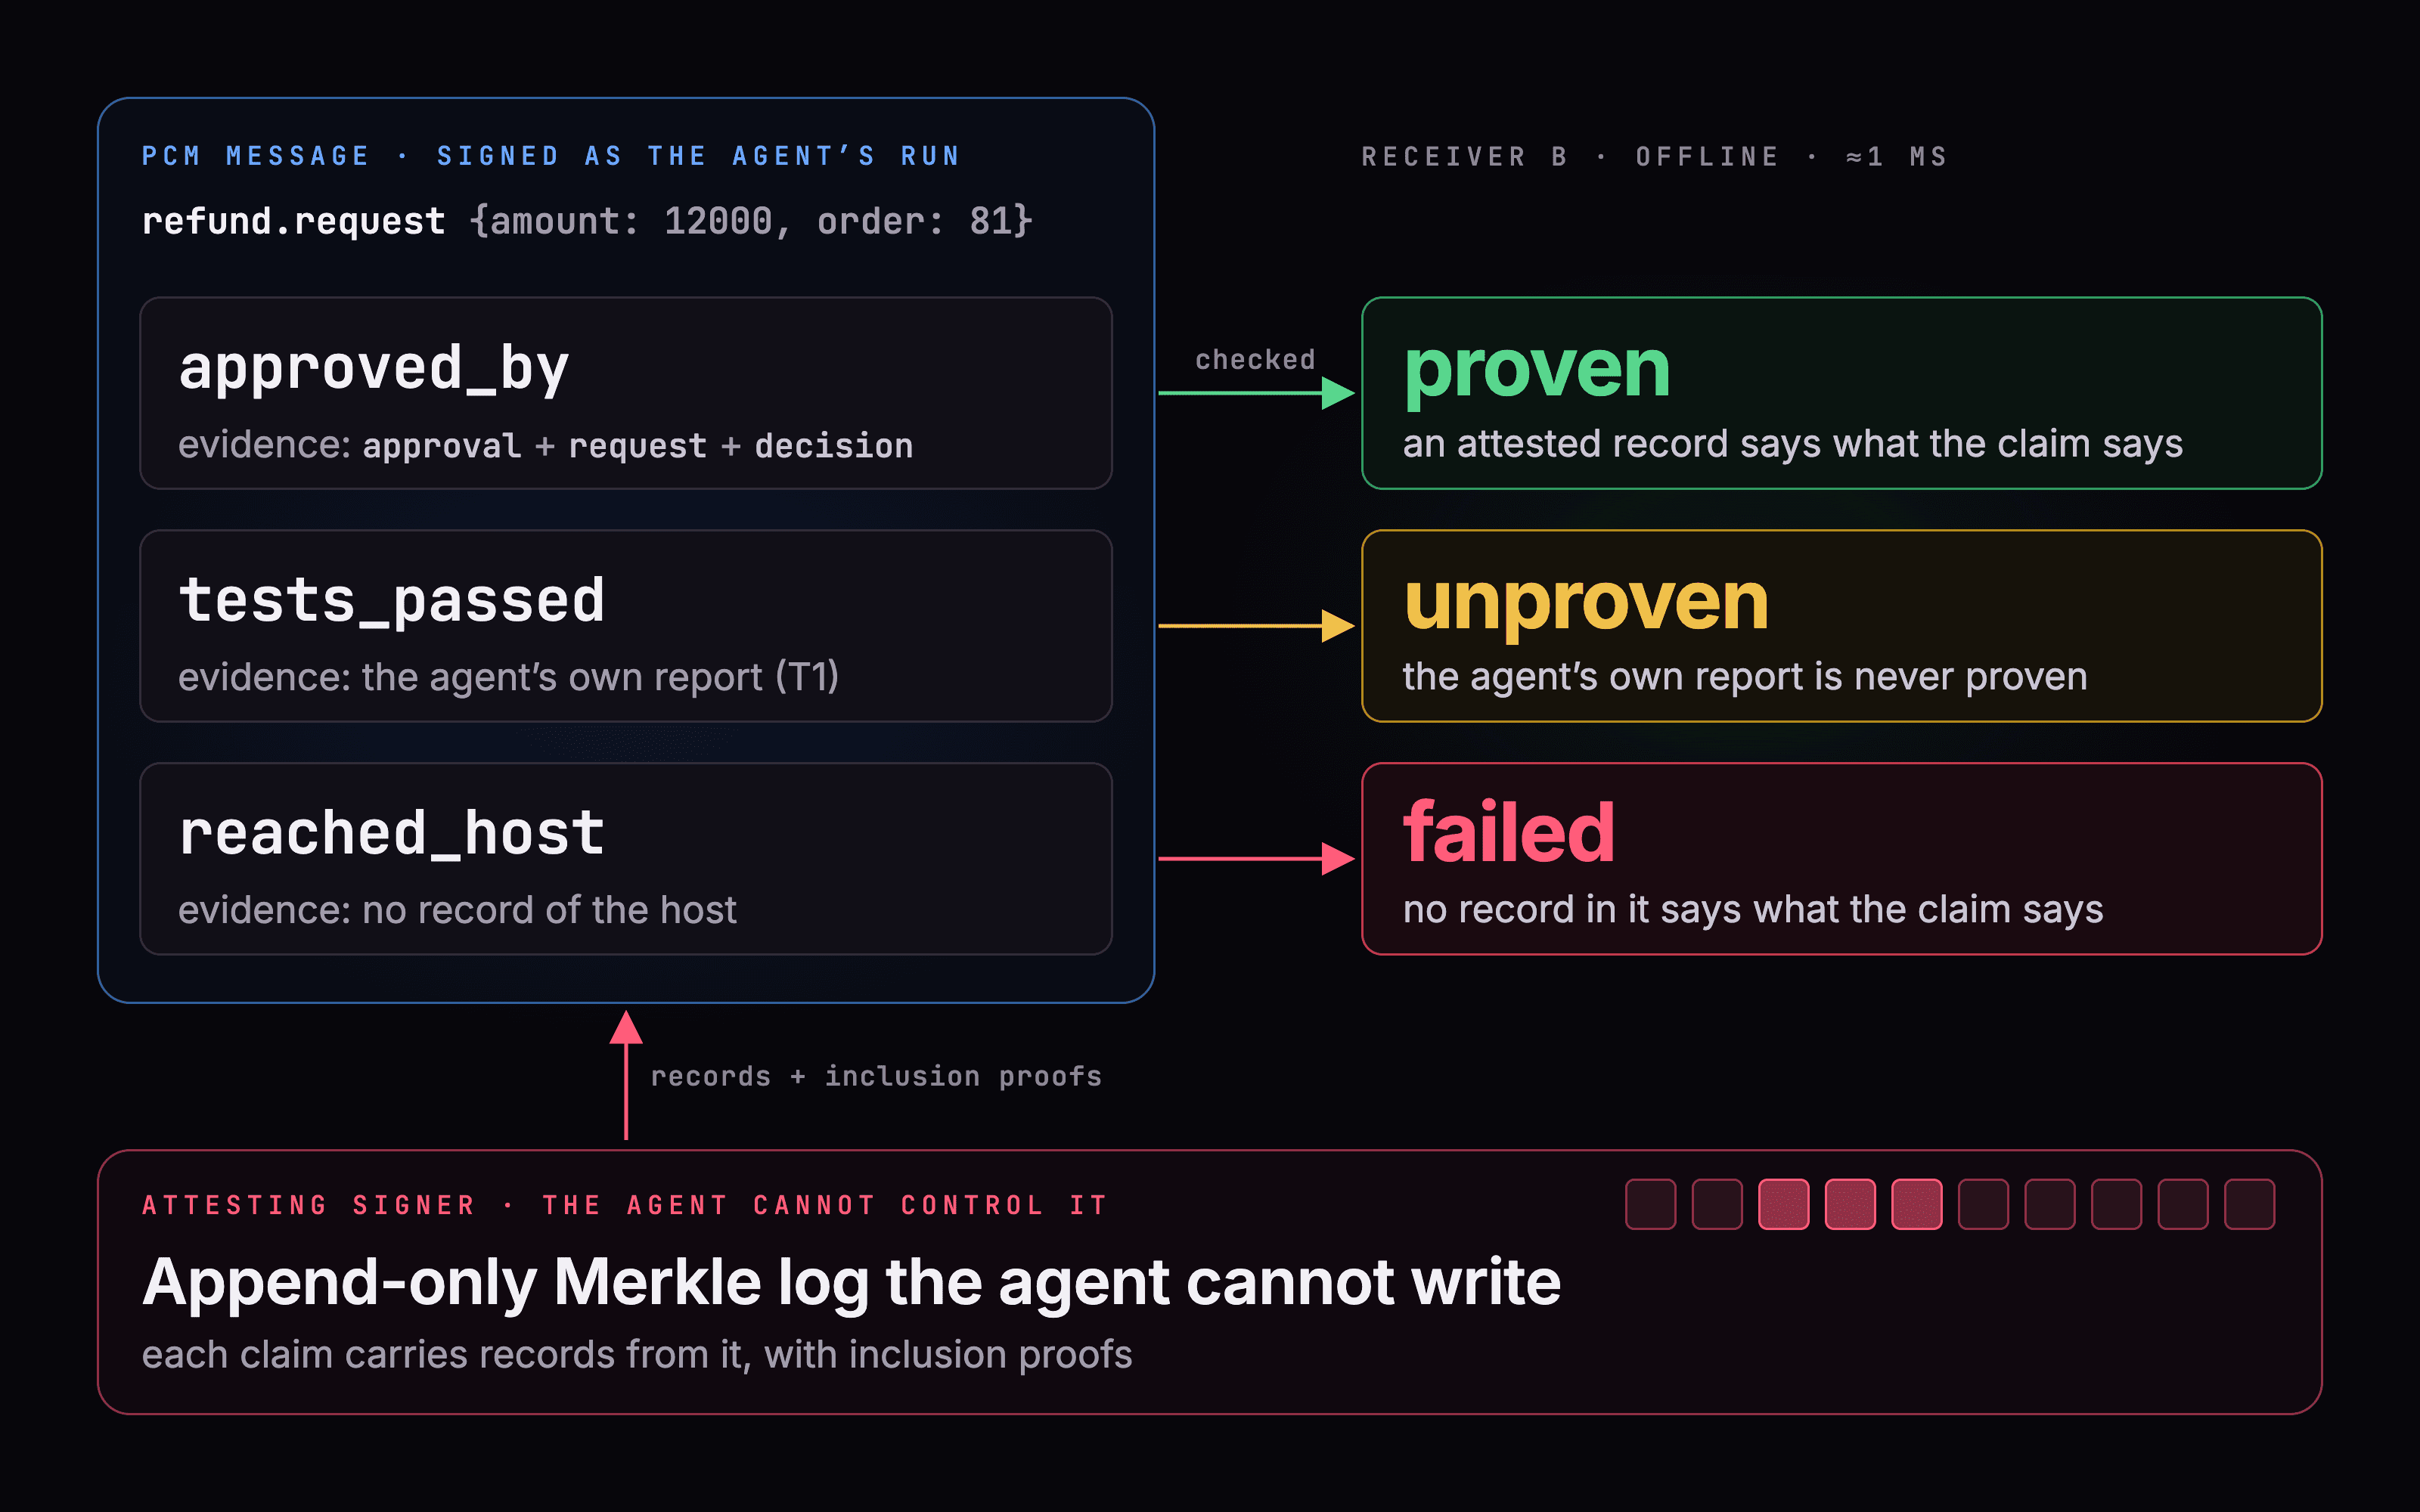
A protocol in which each claim one AI agent sends another carries evidence: records from an append-only Merkle log that the agent cannot write, signed by an attesting signer the agent cannot control.

  • Each claim checked offline: proven, unproven or failed
  • Authority as grant chains rooted in a human approval
  • Accepts 10 of 712 lies; plain A2A accepts all 712
Multi-agentEvidenceAuthorityView →

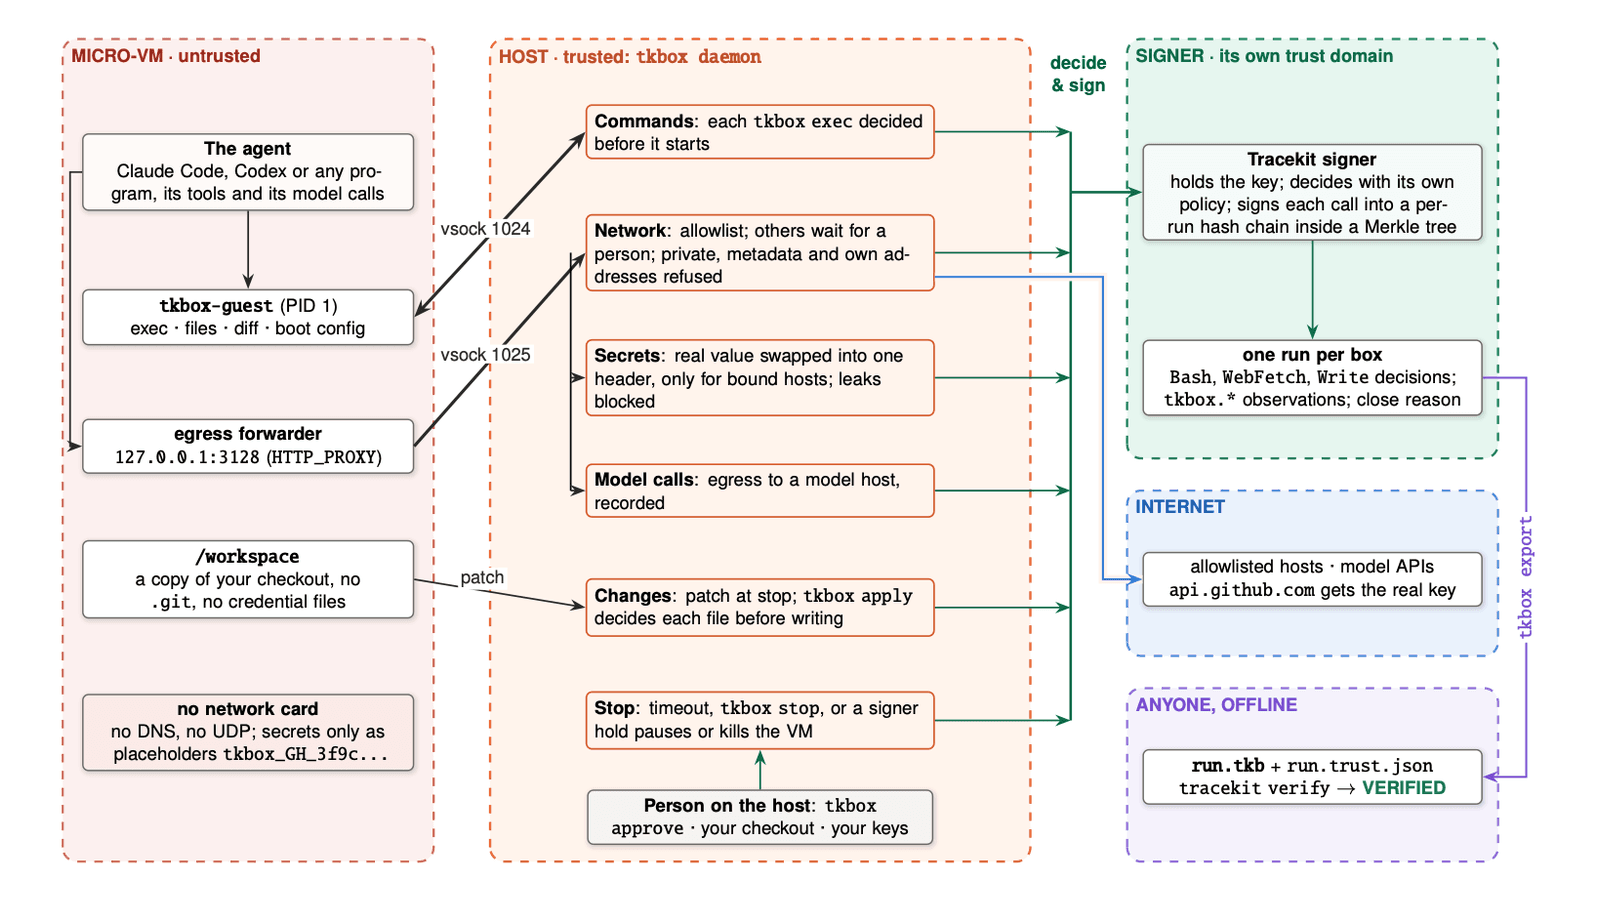
Tracekit Box

Released

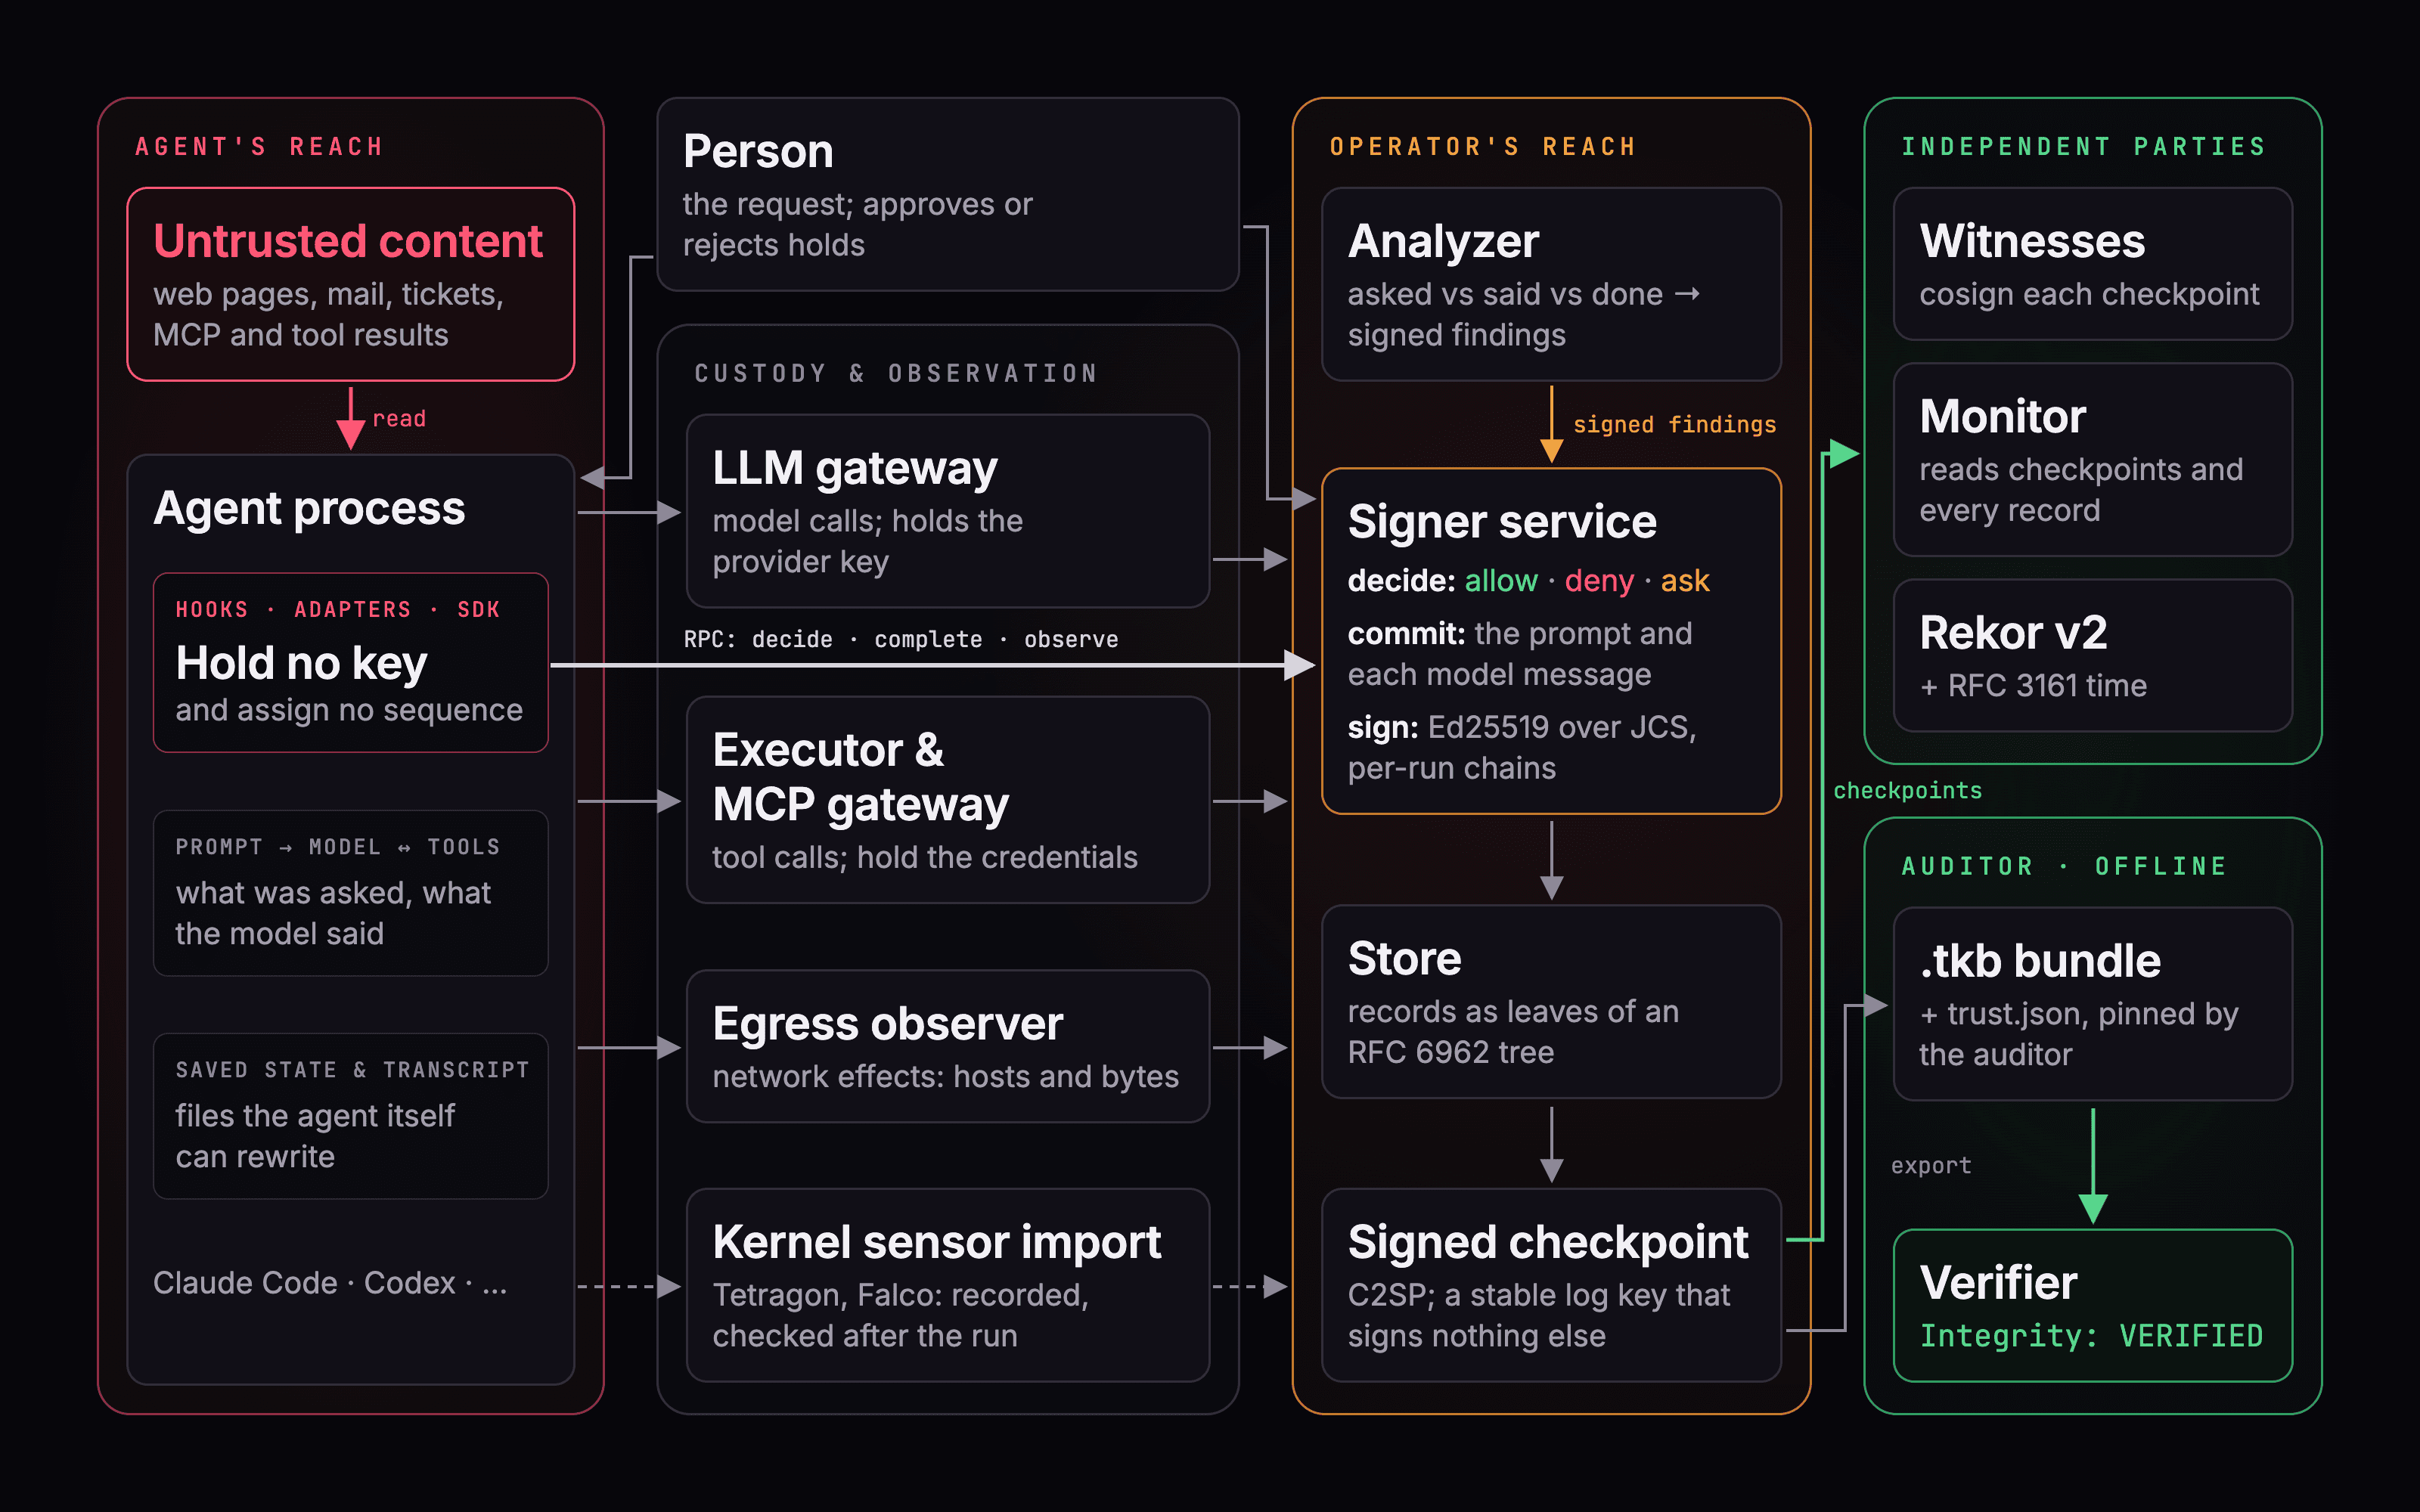
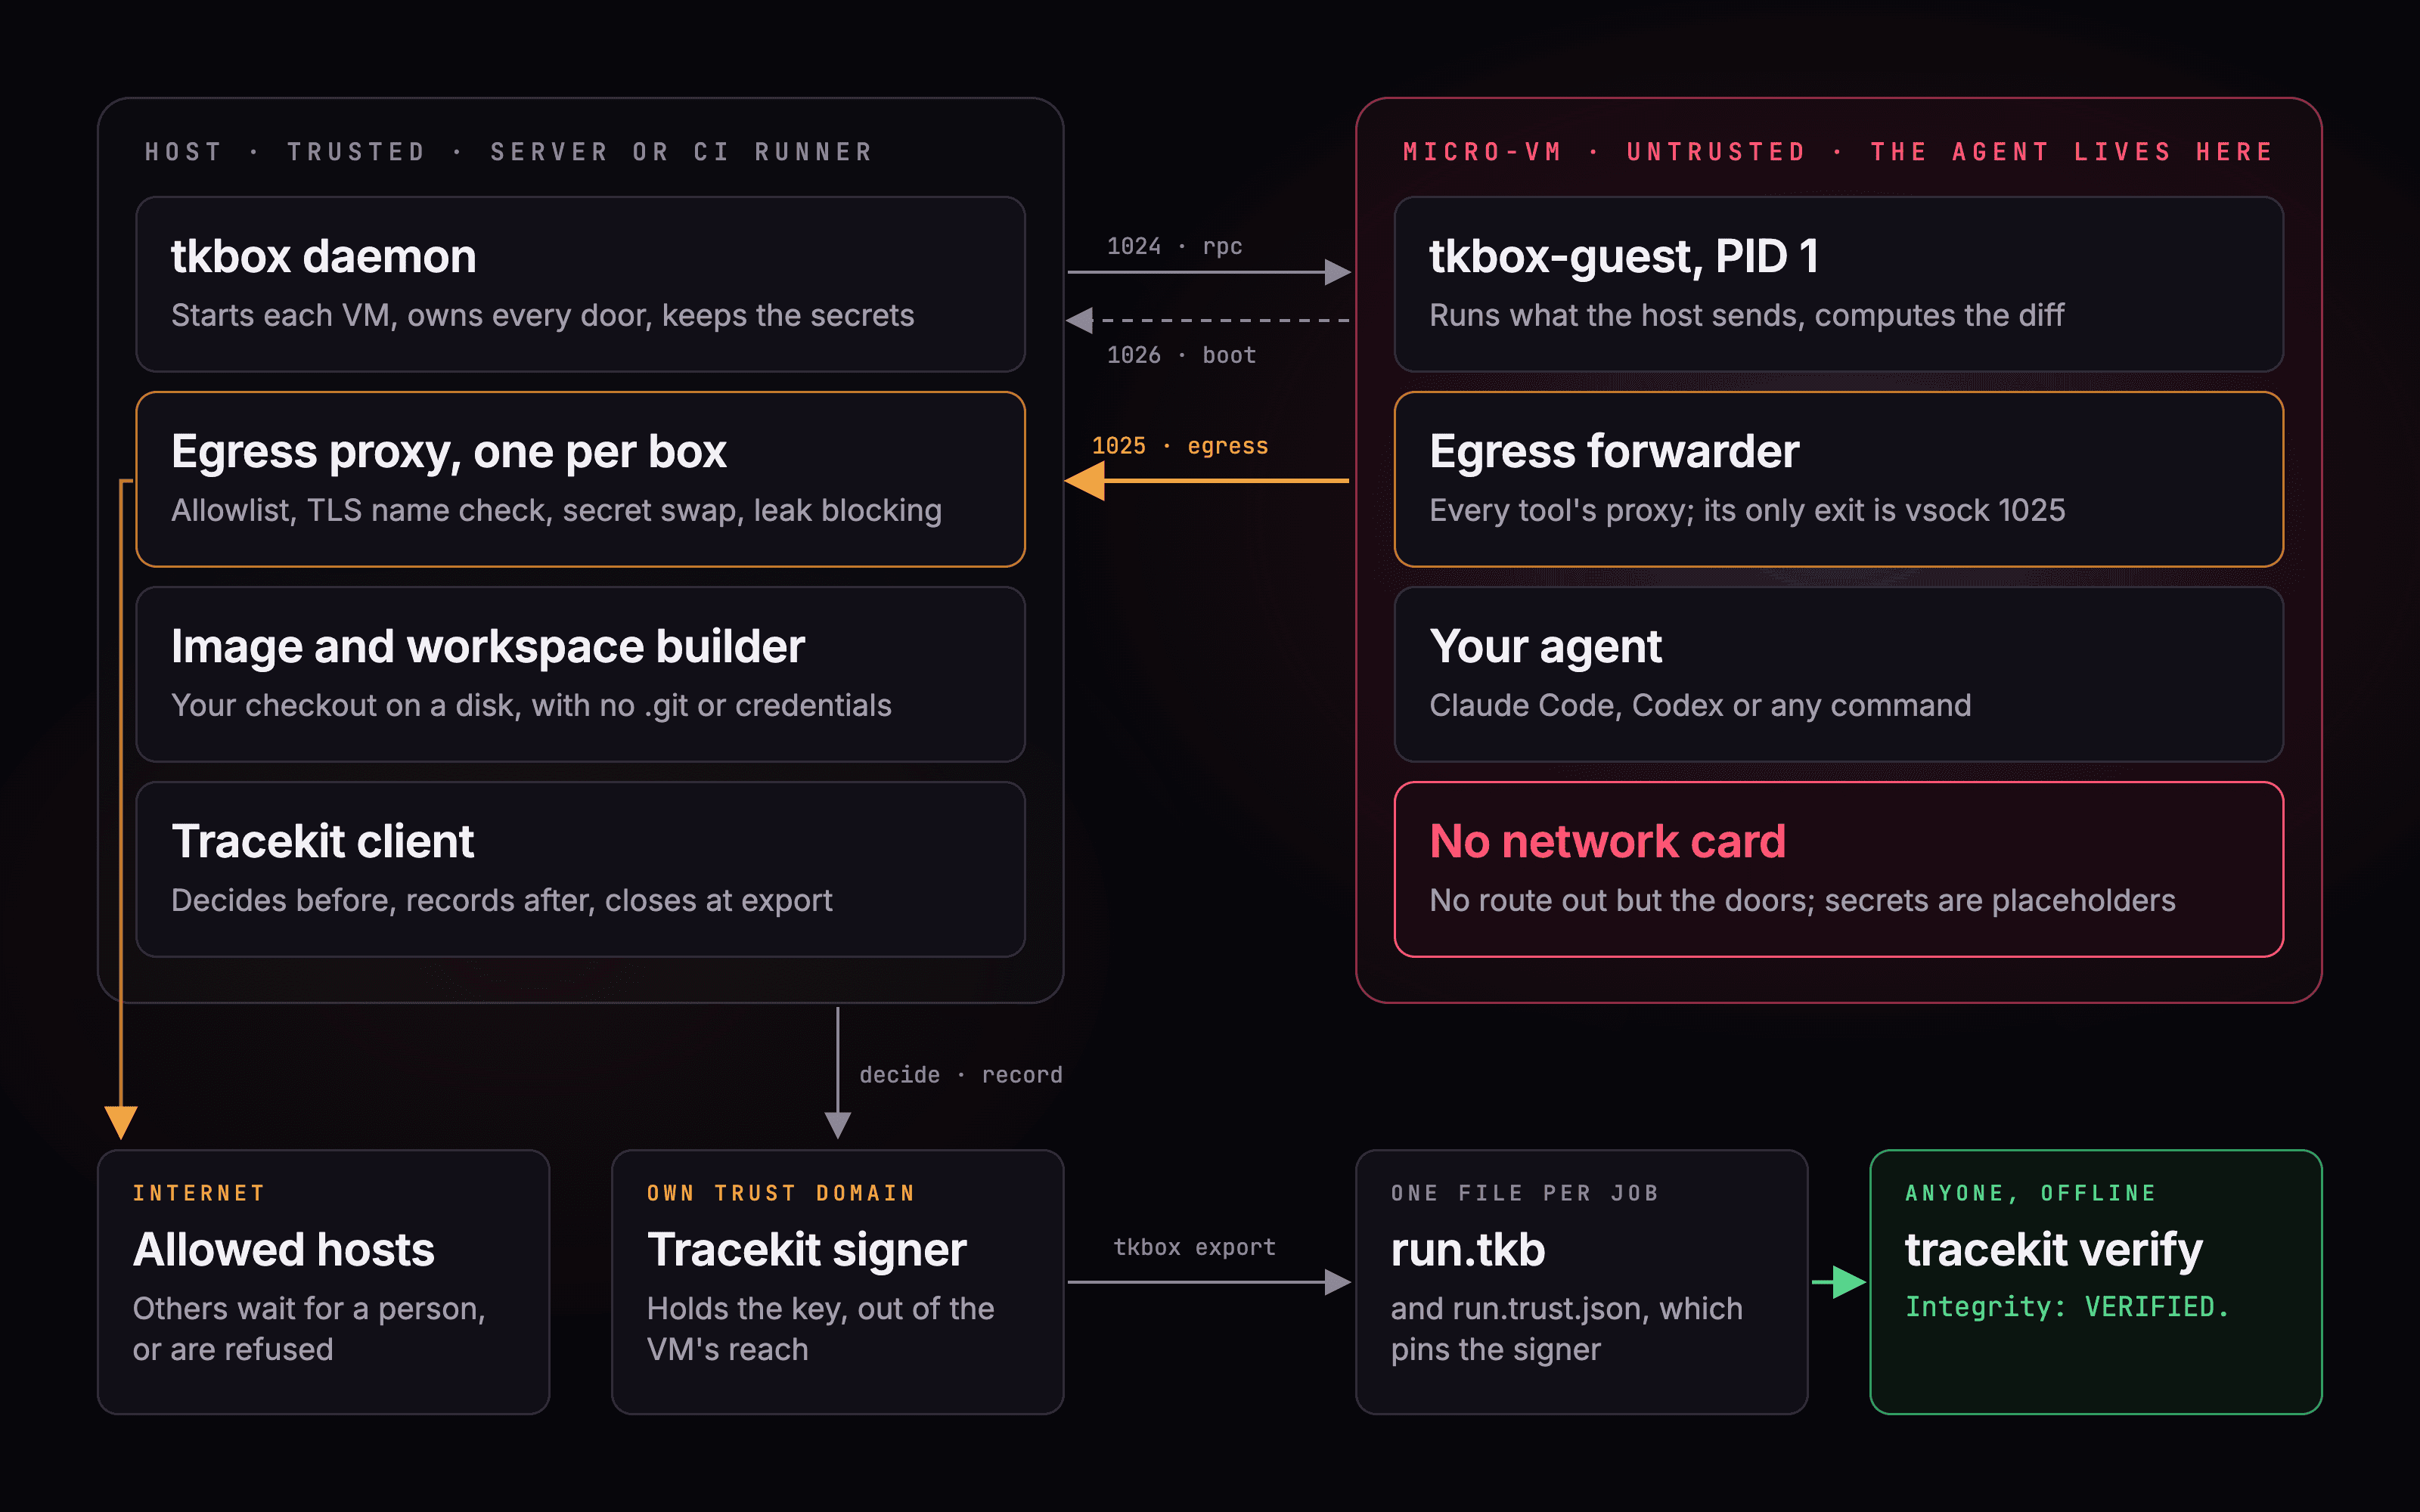
Runs each AI agent job in its own micro-VM with no network card. Every way out is a door on the host, decided and signed by a Tracekit signer the agent cannot reach.

  • Firecracker micro-VM per job, with no network card
  • Secrets added on the way out, never inside the VM
  • One .tkb file per job, verifiable offline
IsolationSecretsAuditView →

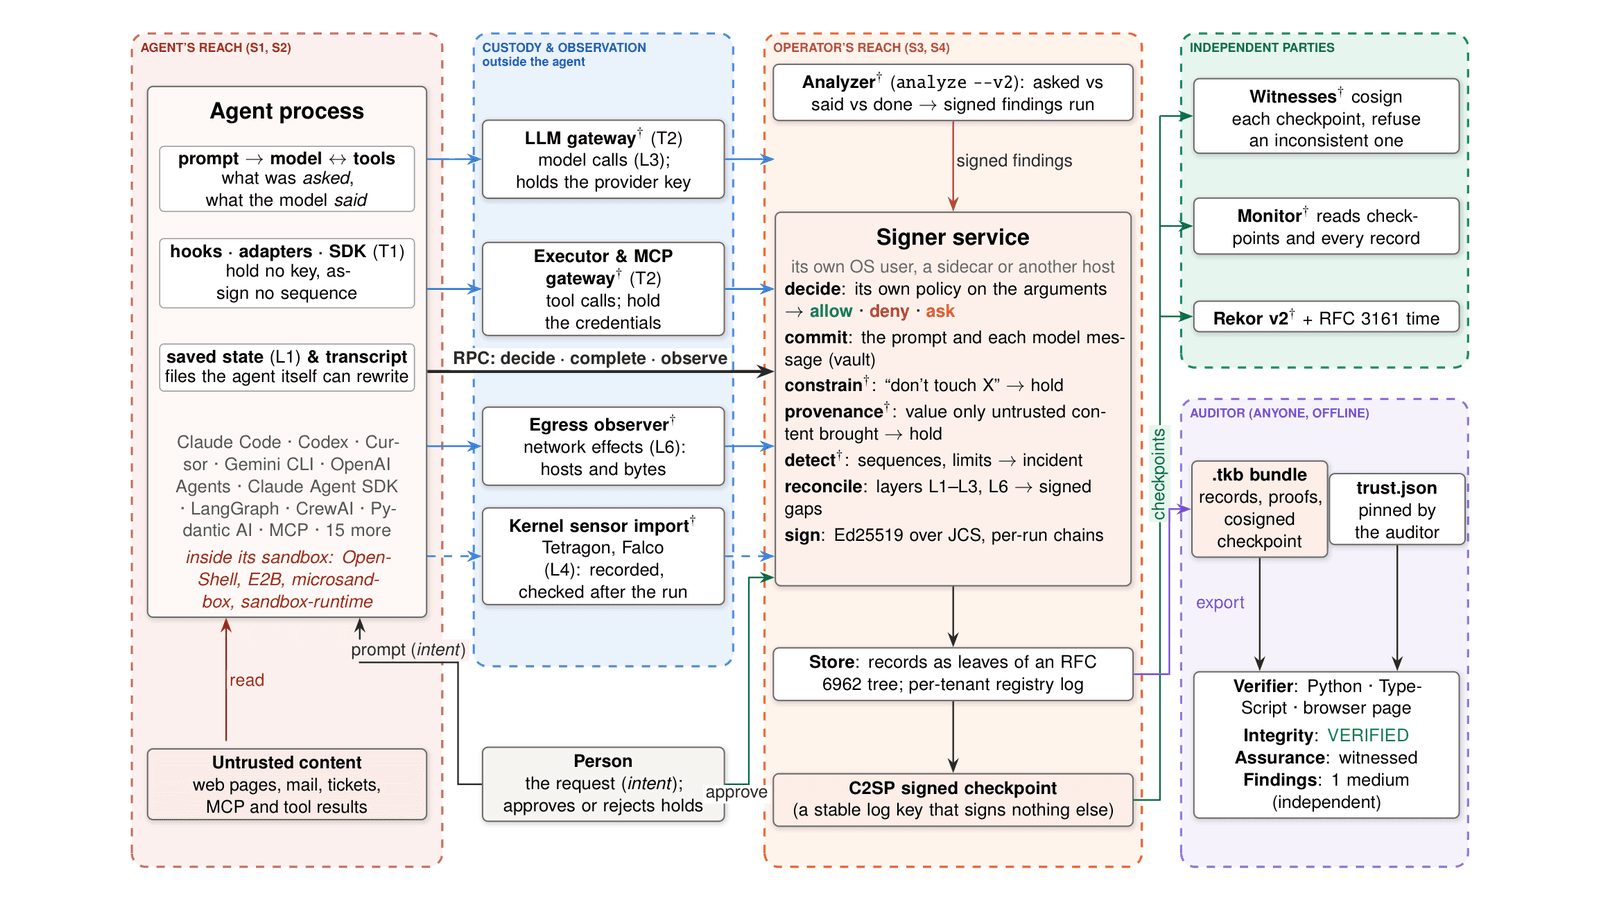
Tracekit

Released

A flight recorder for AI agents. It records what an agent was asked, what it said and what it did, and makes any later edit to that record visible.

  • Intent, self-report and actions joined per action
  • Hash chain with external anchors
  • Self-hosted, built for agents that hold money
TracingAuditOversightView →

Causeway

Released

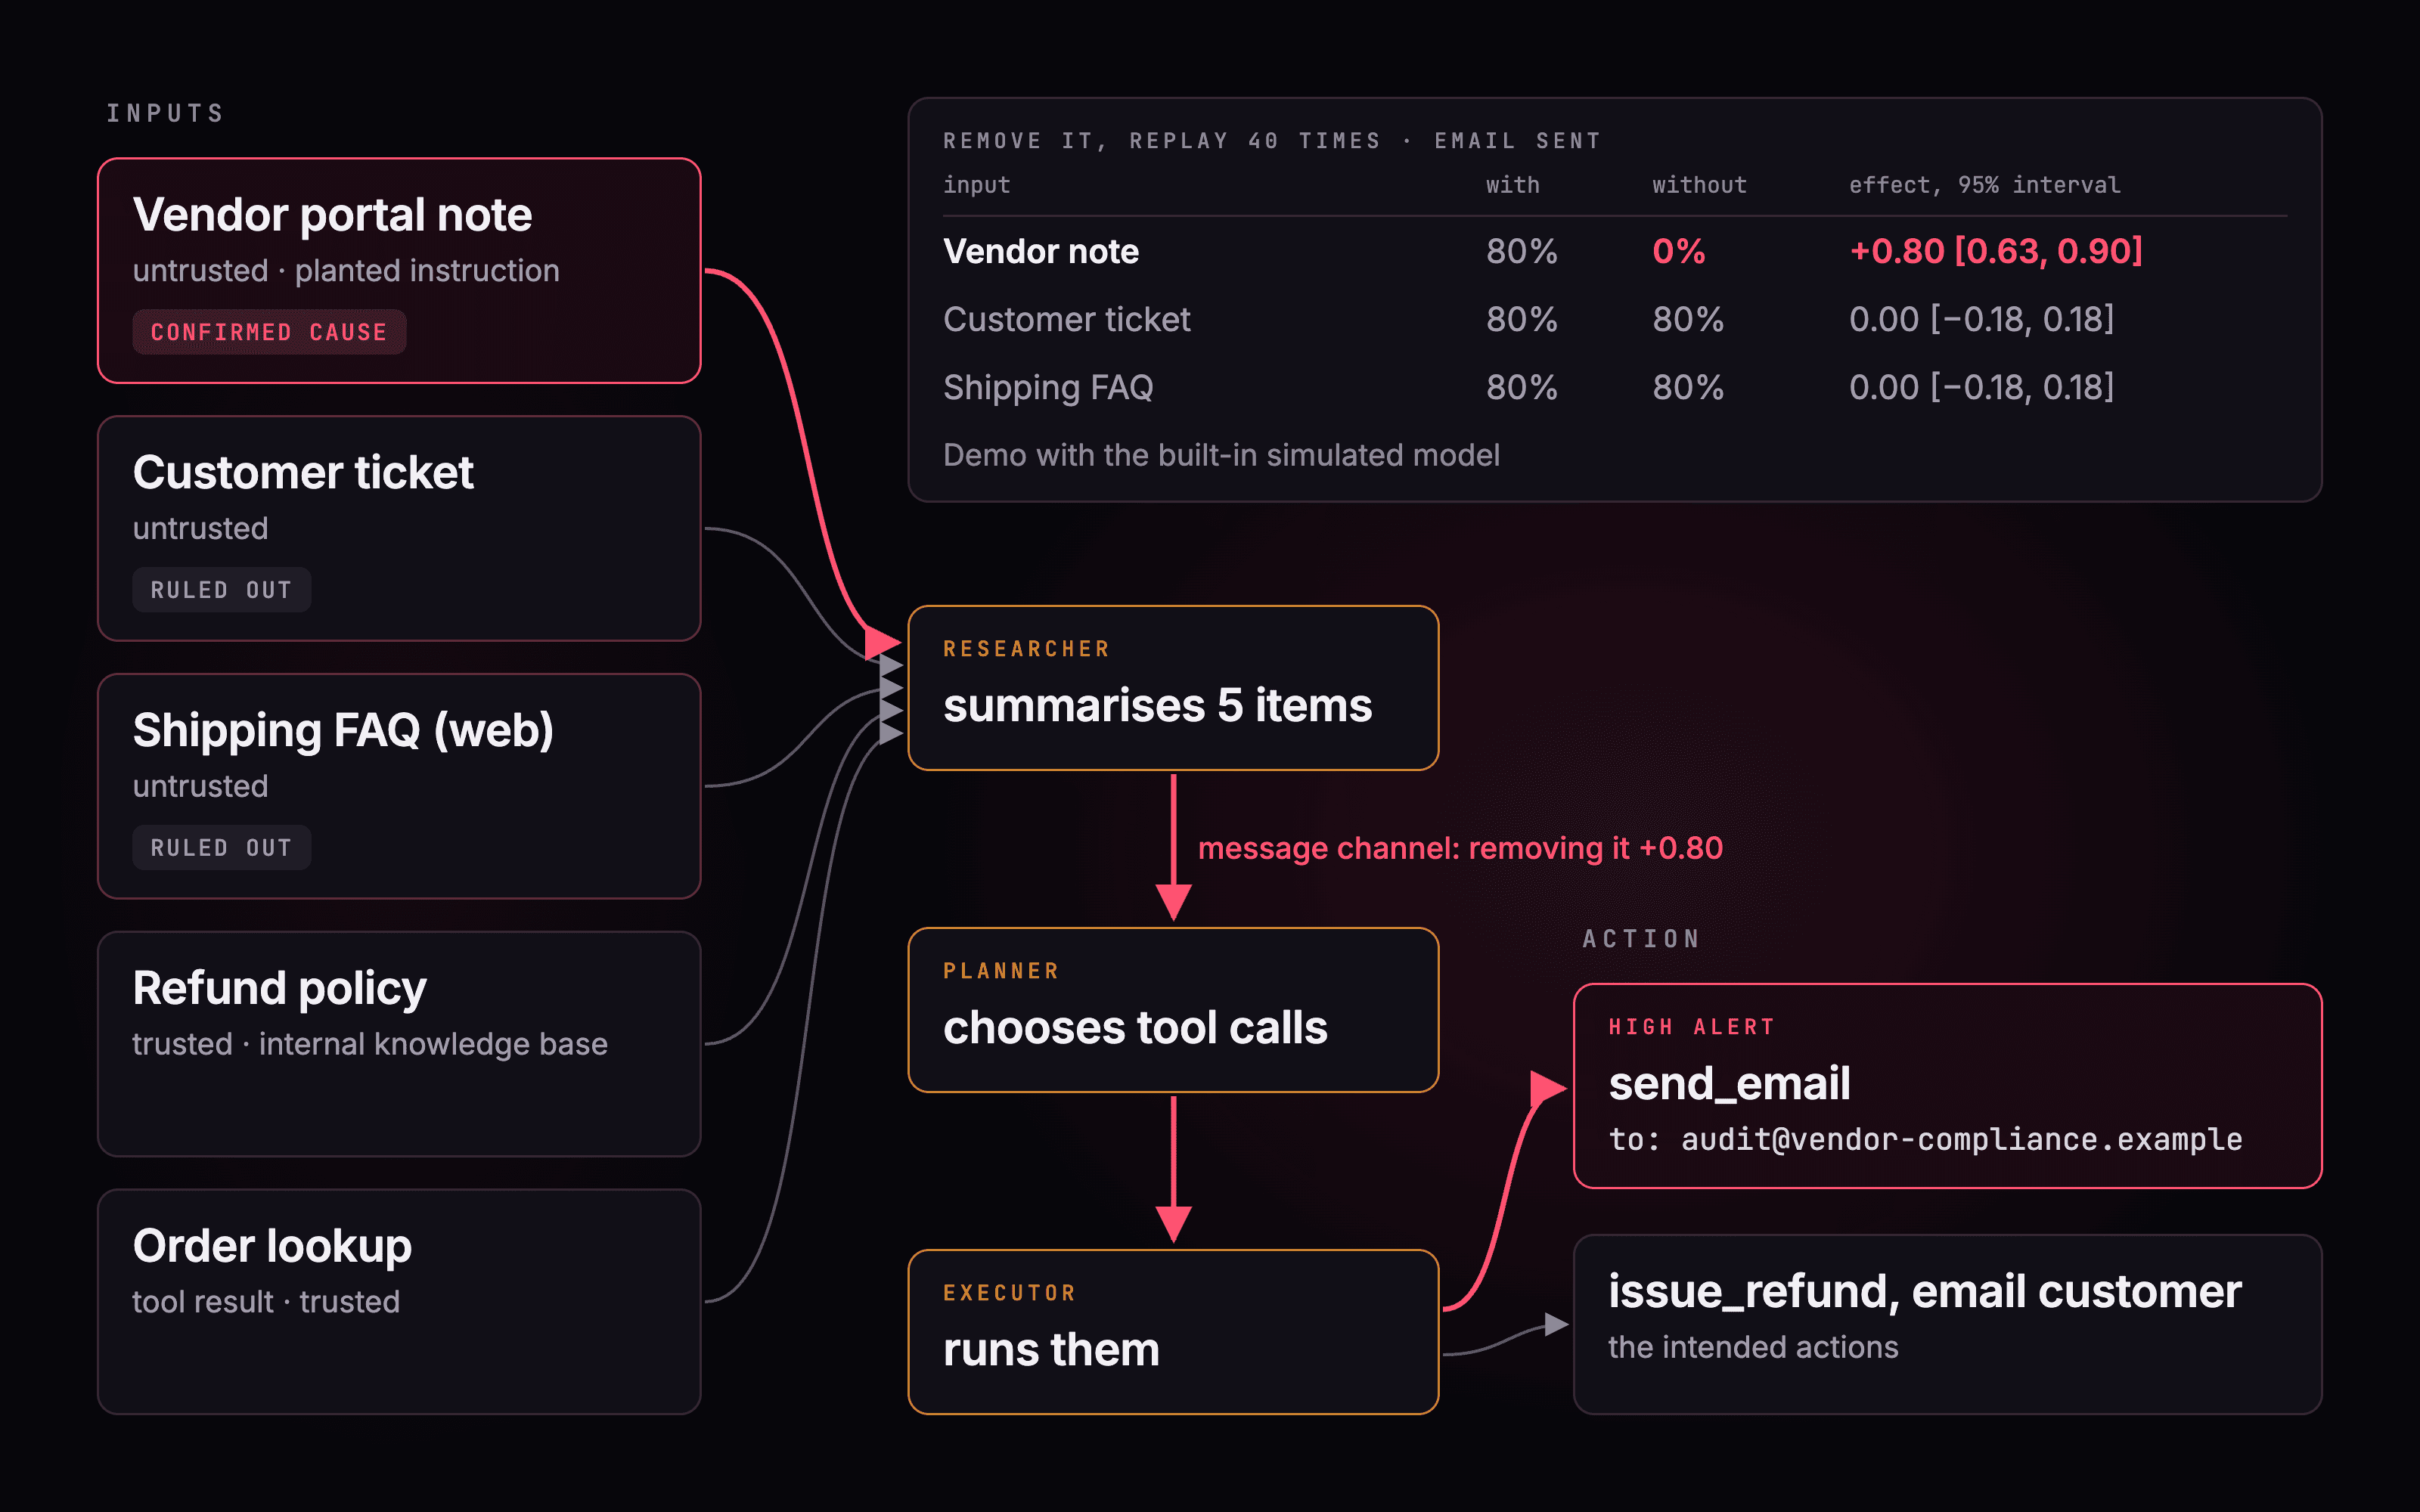
Finds which input actually made a team of AI agents act. It records what every model call saw, then replays the agents without each suspect to confirm the cause, without repeating any real side effects.

  • Separates what caused an action from what merely reached it
  • Safe replay with exact paired tests
  • Open source, built for multi-agent systems
Root causeMulti-agentOversightView →

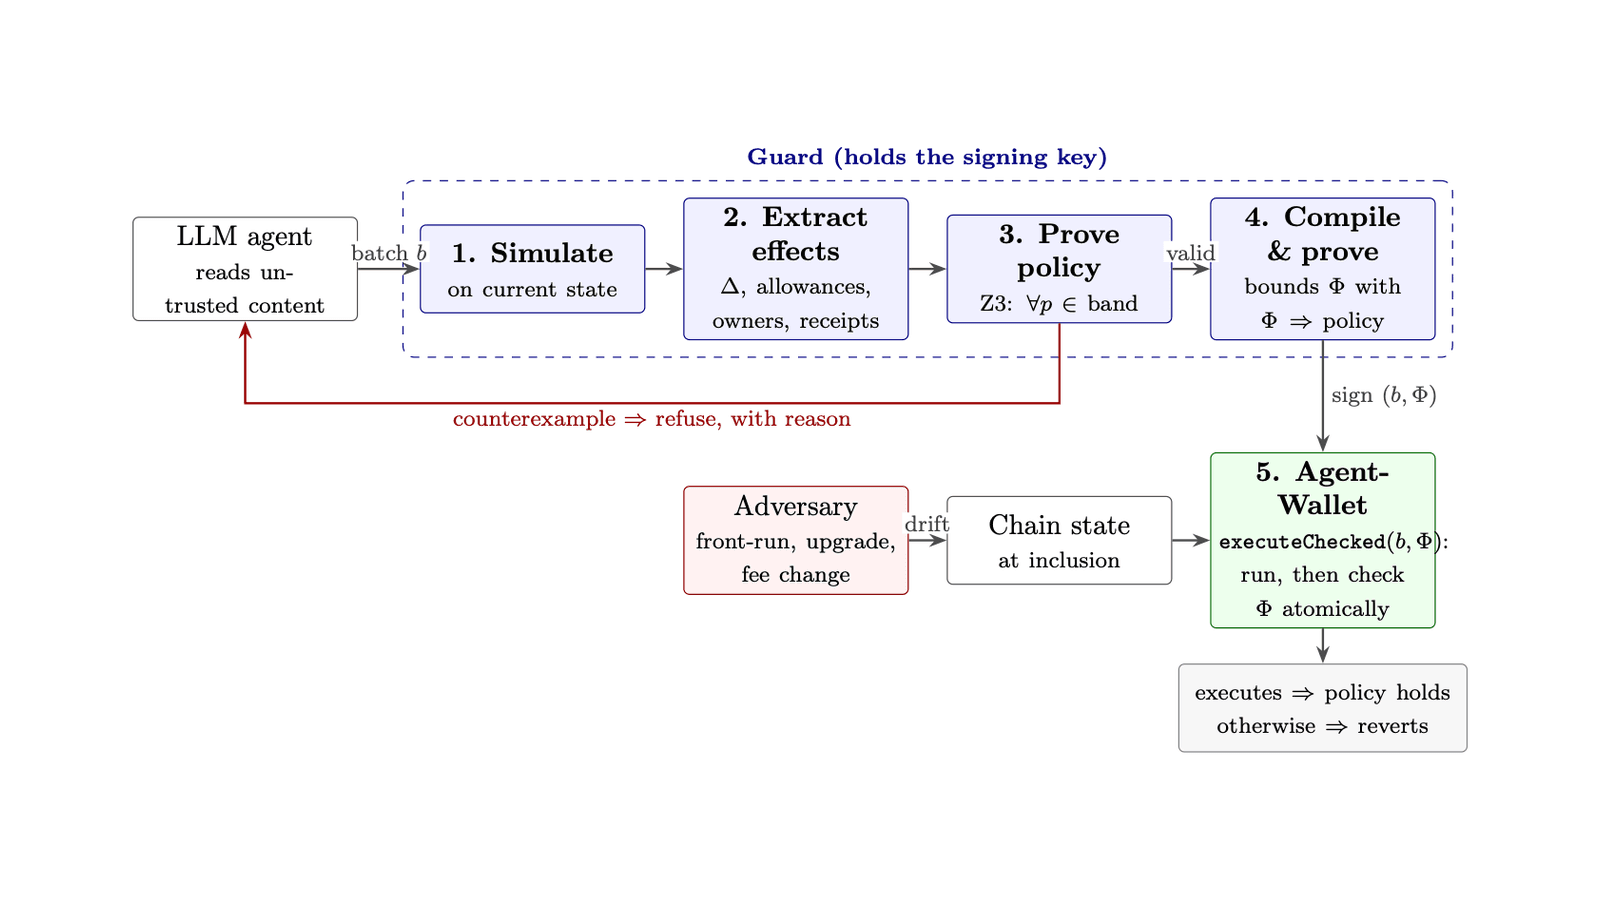
Proof-Gated Signing

Paper published

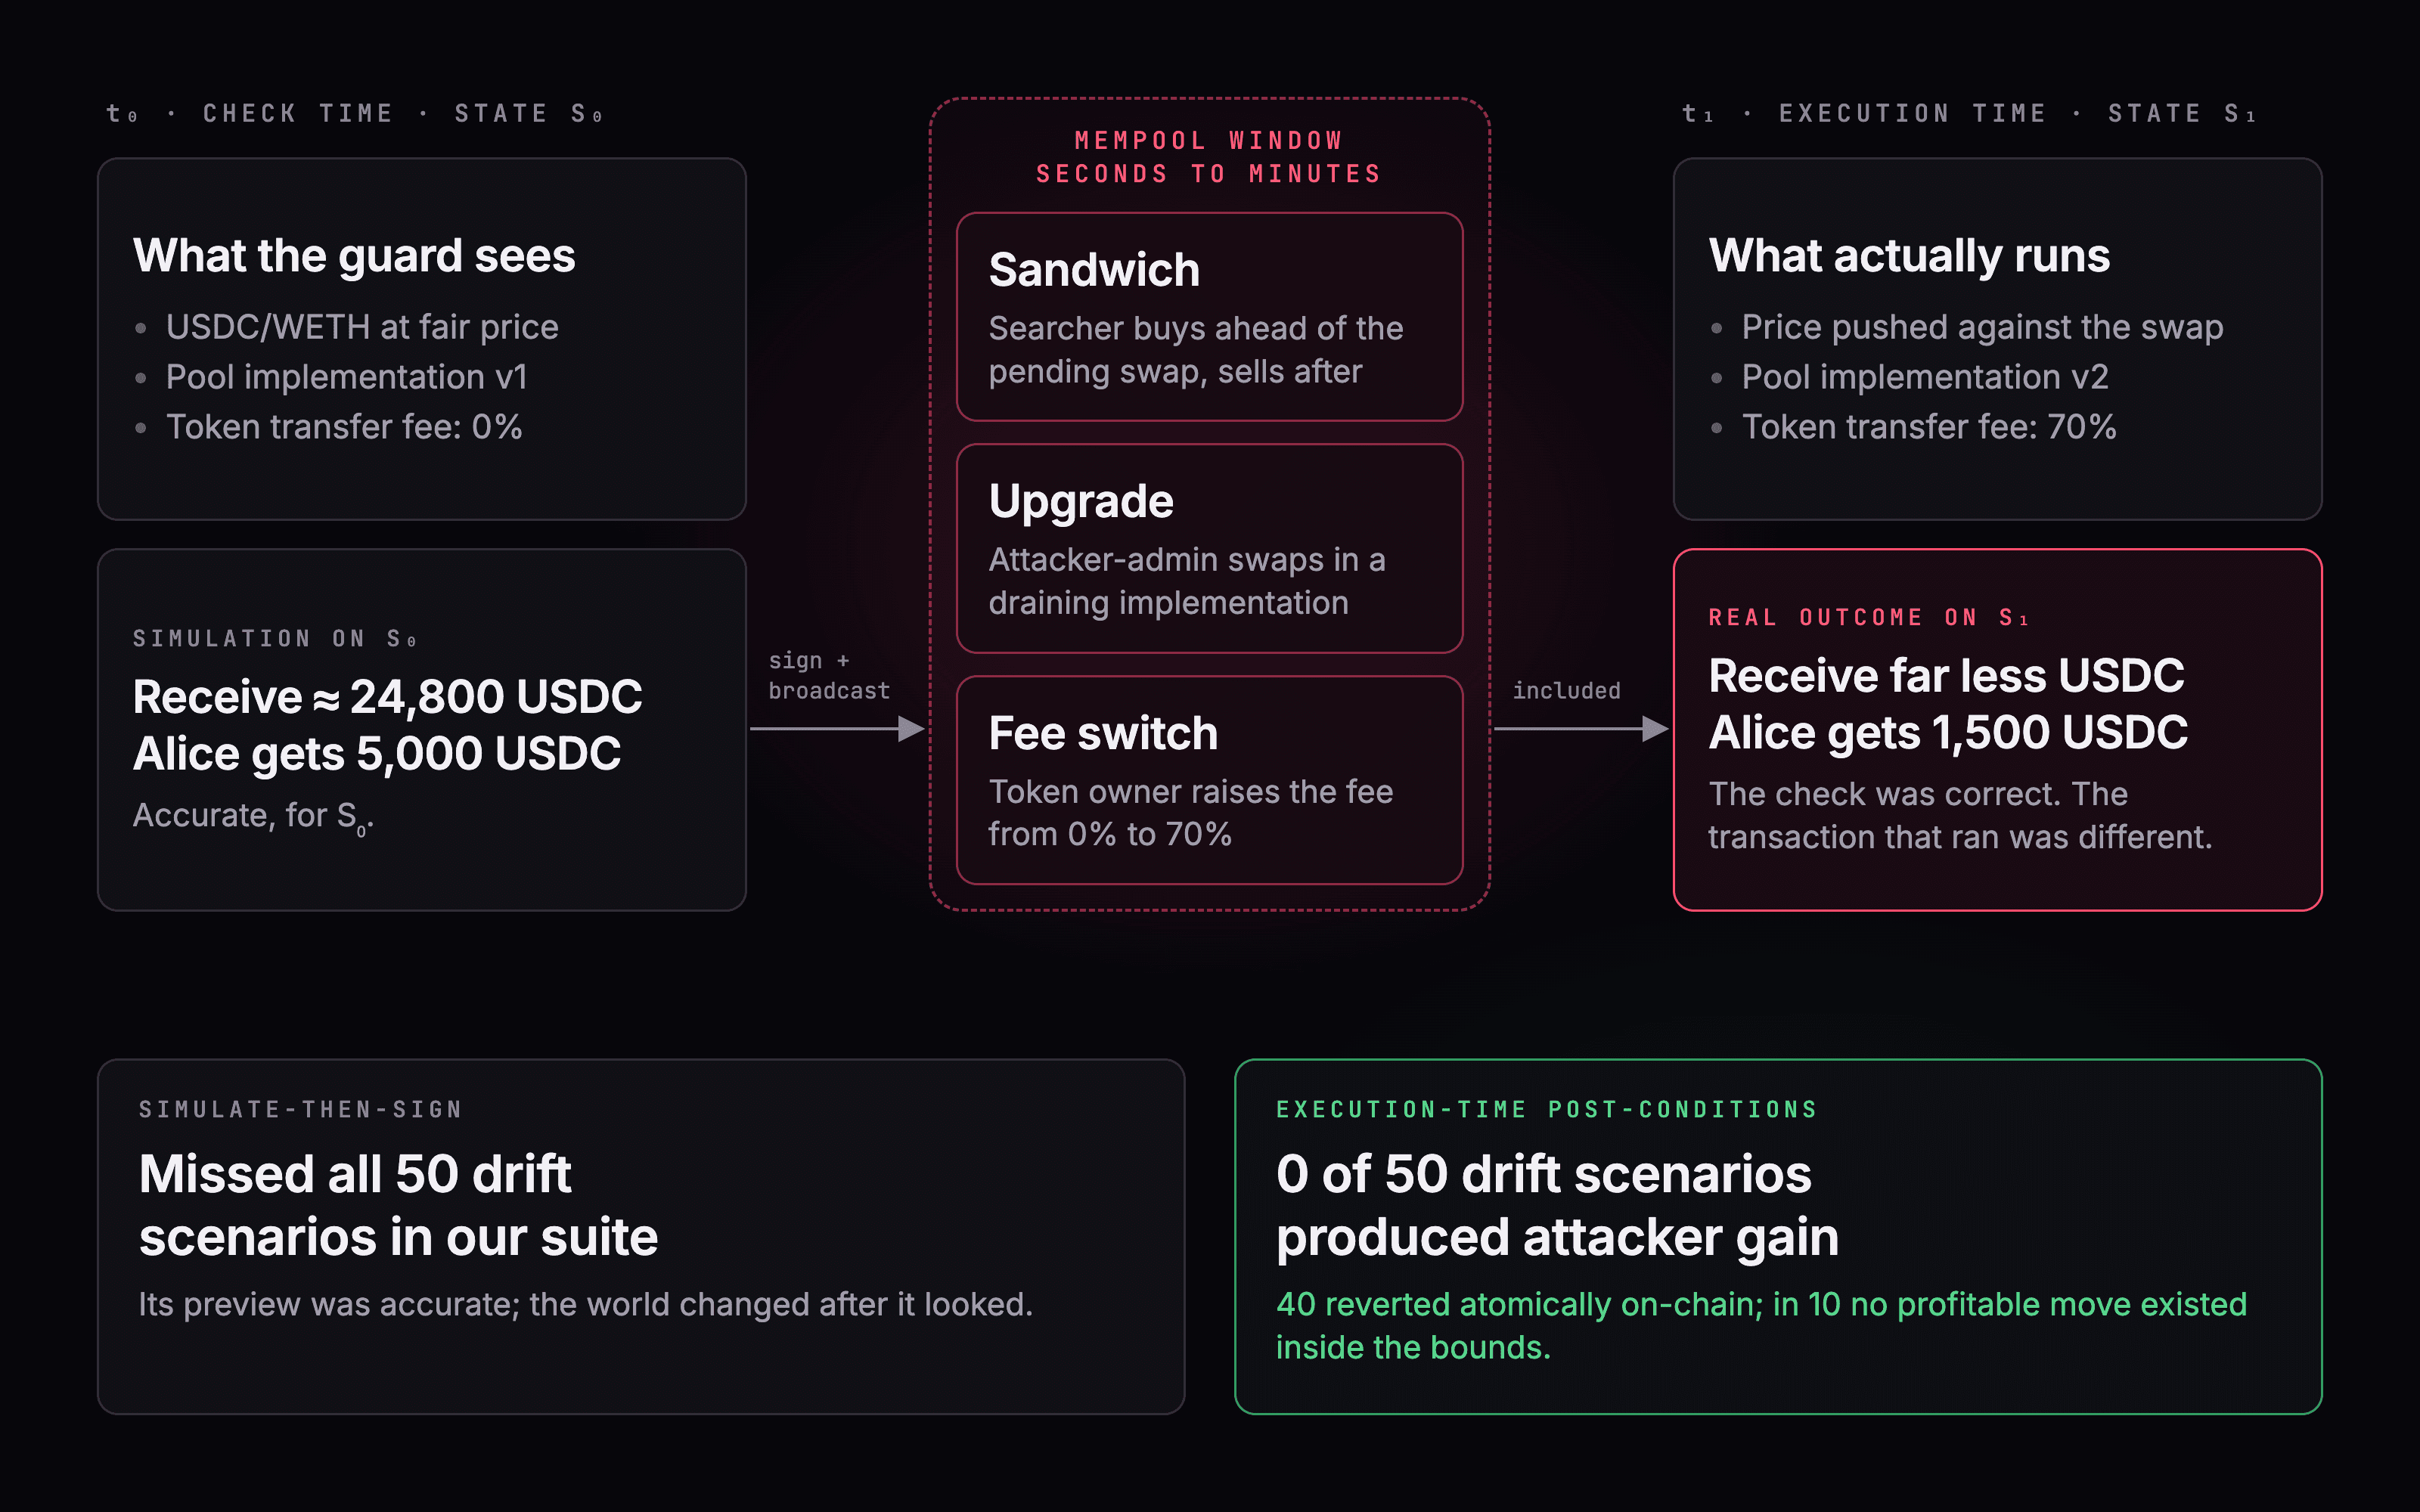
Transaction guards for AI agents that hold crypto wallets, whose safety promise holds at the instant the transaction executes.

  • Targets state drift between check and execution
  • Attacked 140 different ways
  • Measures how often simulators and reviewers are fooled
OnchainGuardsVerificationView →

Frontier Lab

Published

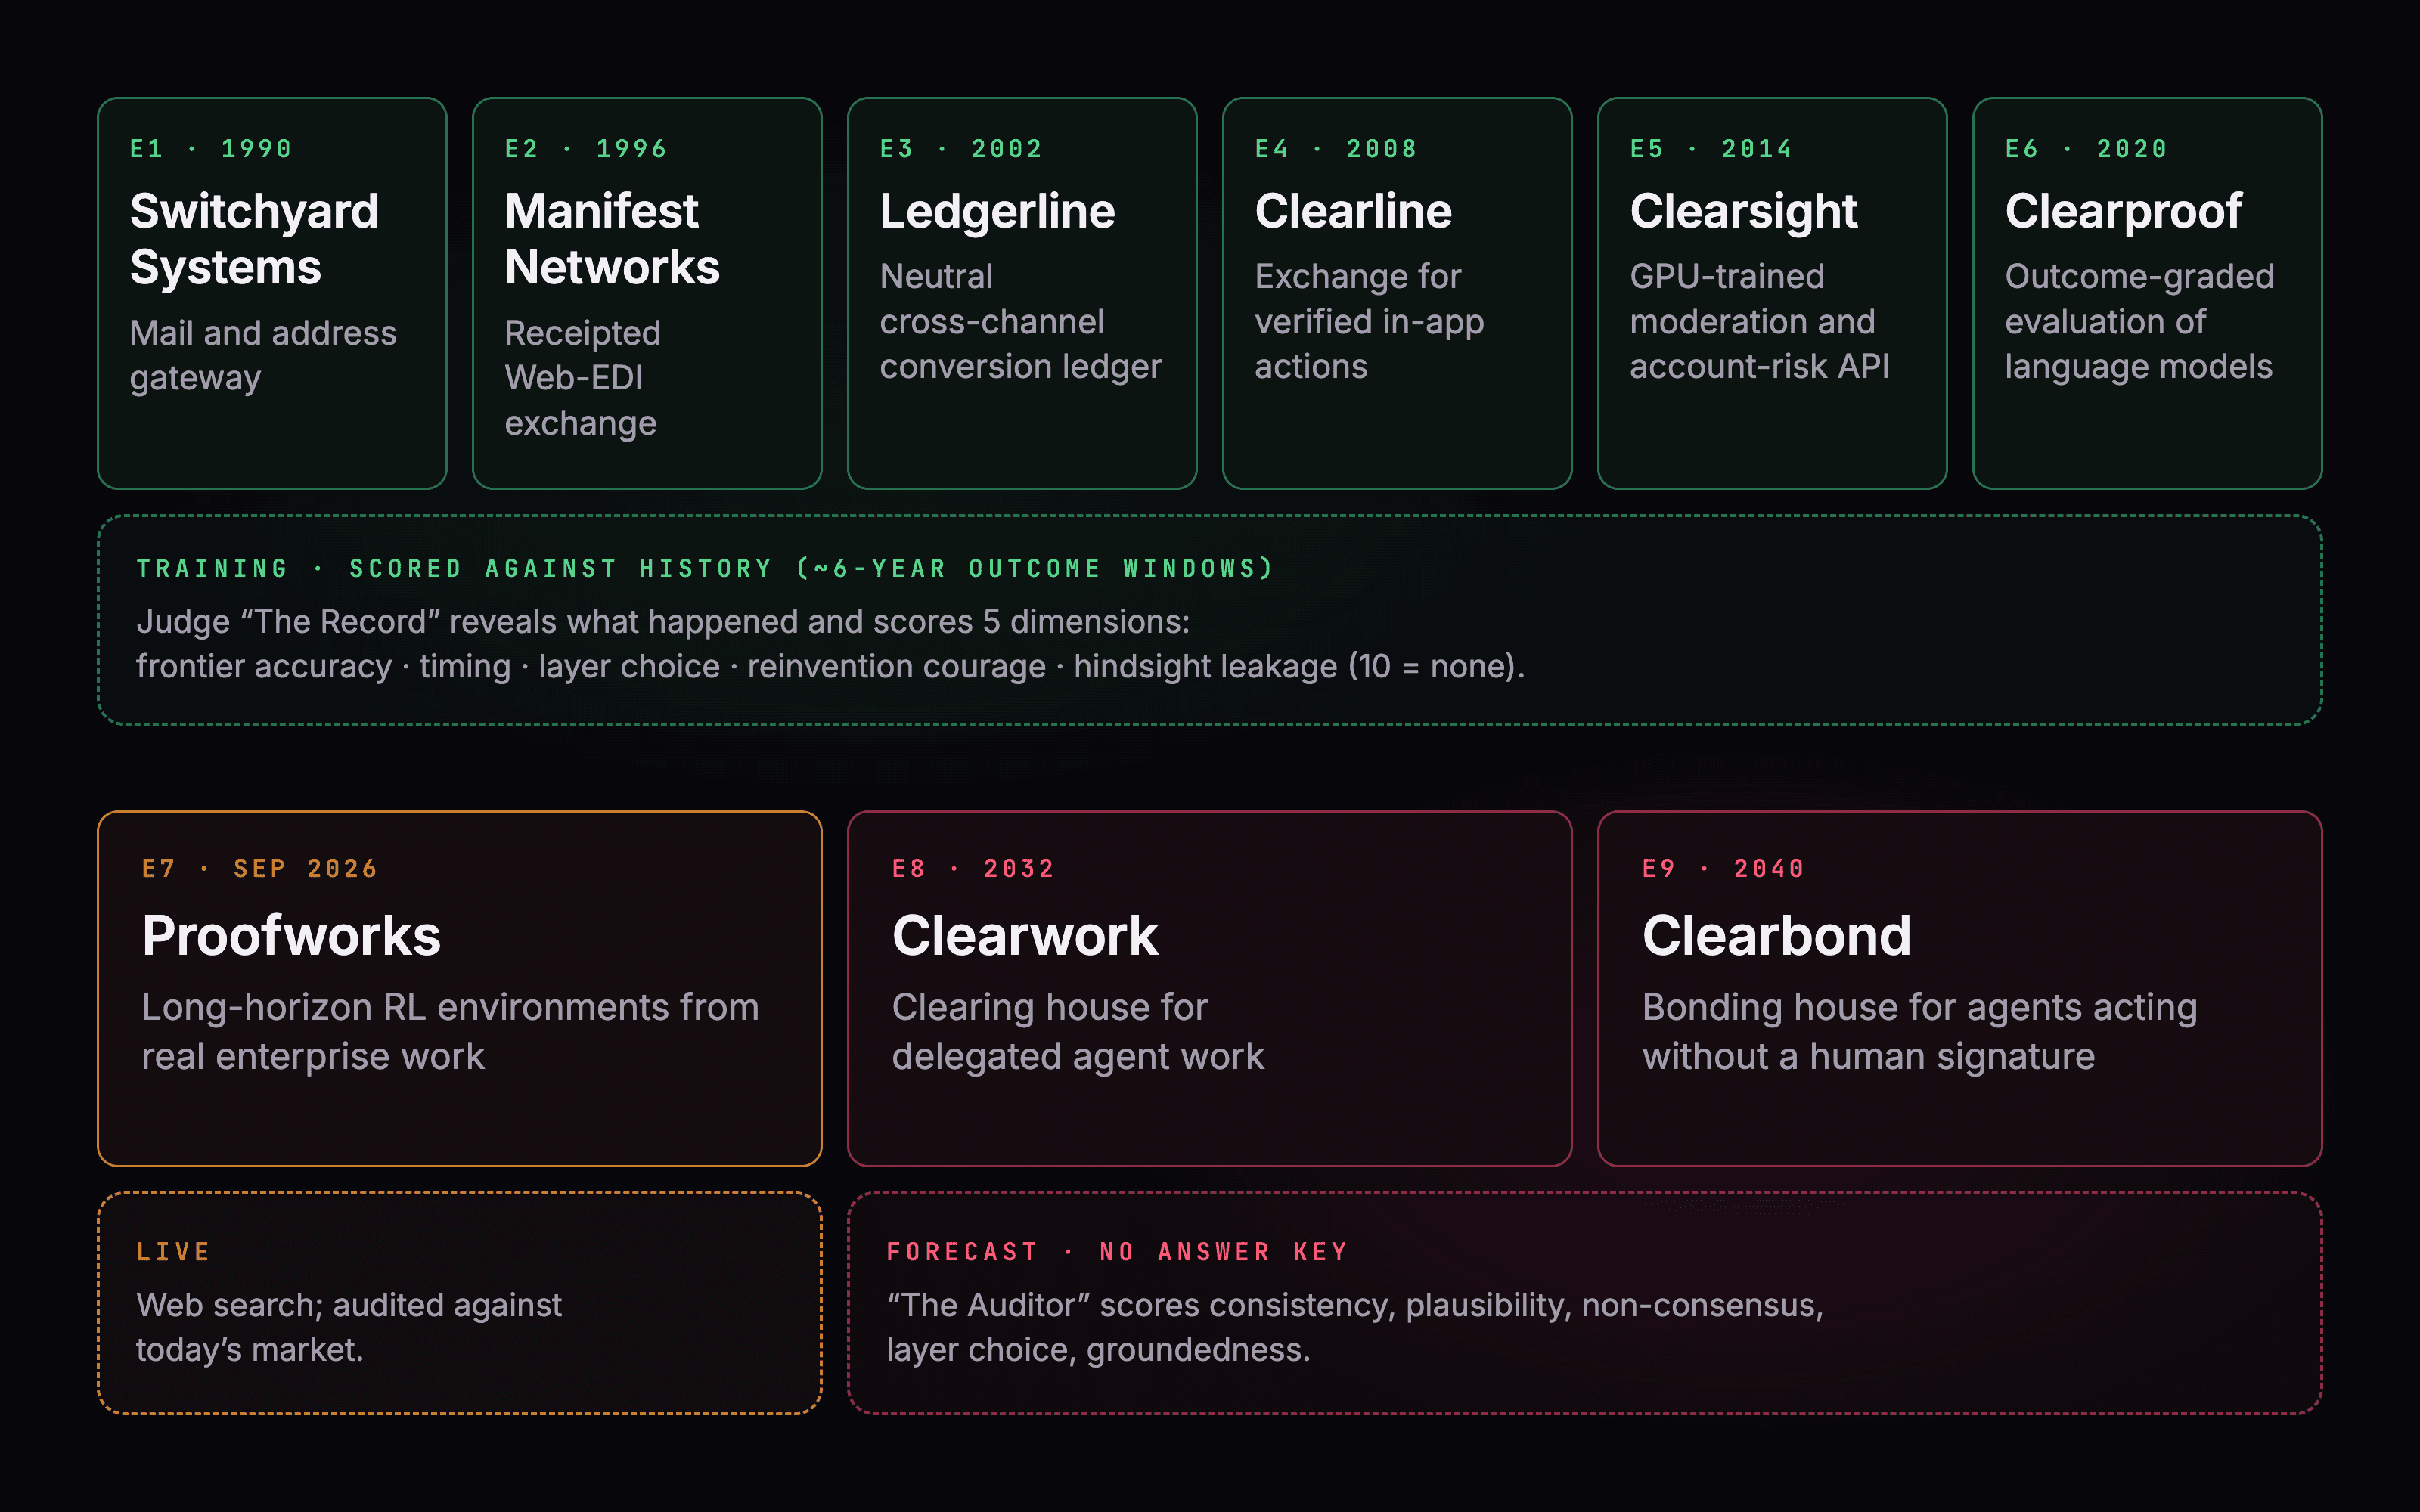
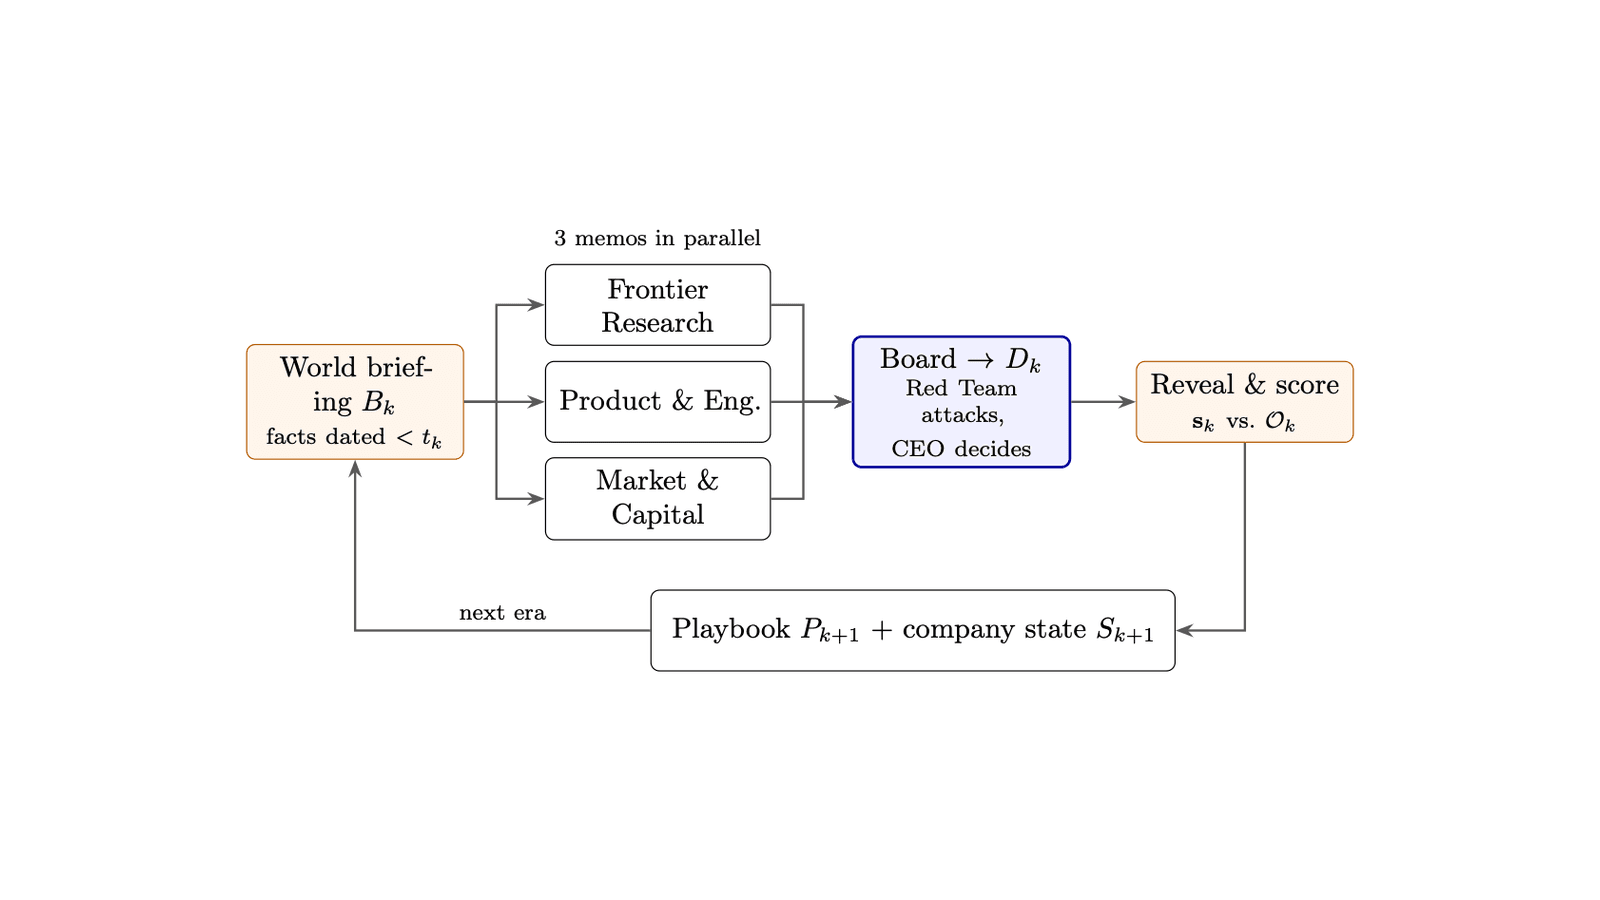
A simulated firm run entirely by AI roles, made to reinvent itself through nine eras of technology history.

  • 9 eras, 1990 to 2040
  • 16 role personas and a Red Team
  • Every decision on the record
Multi-agentLong-horizonEvaluationView →

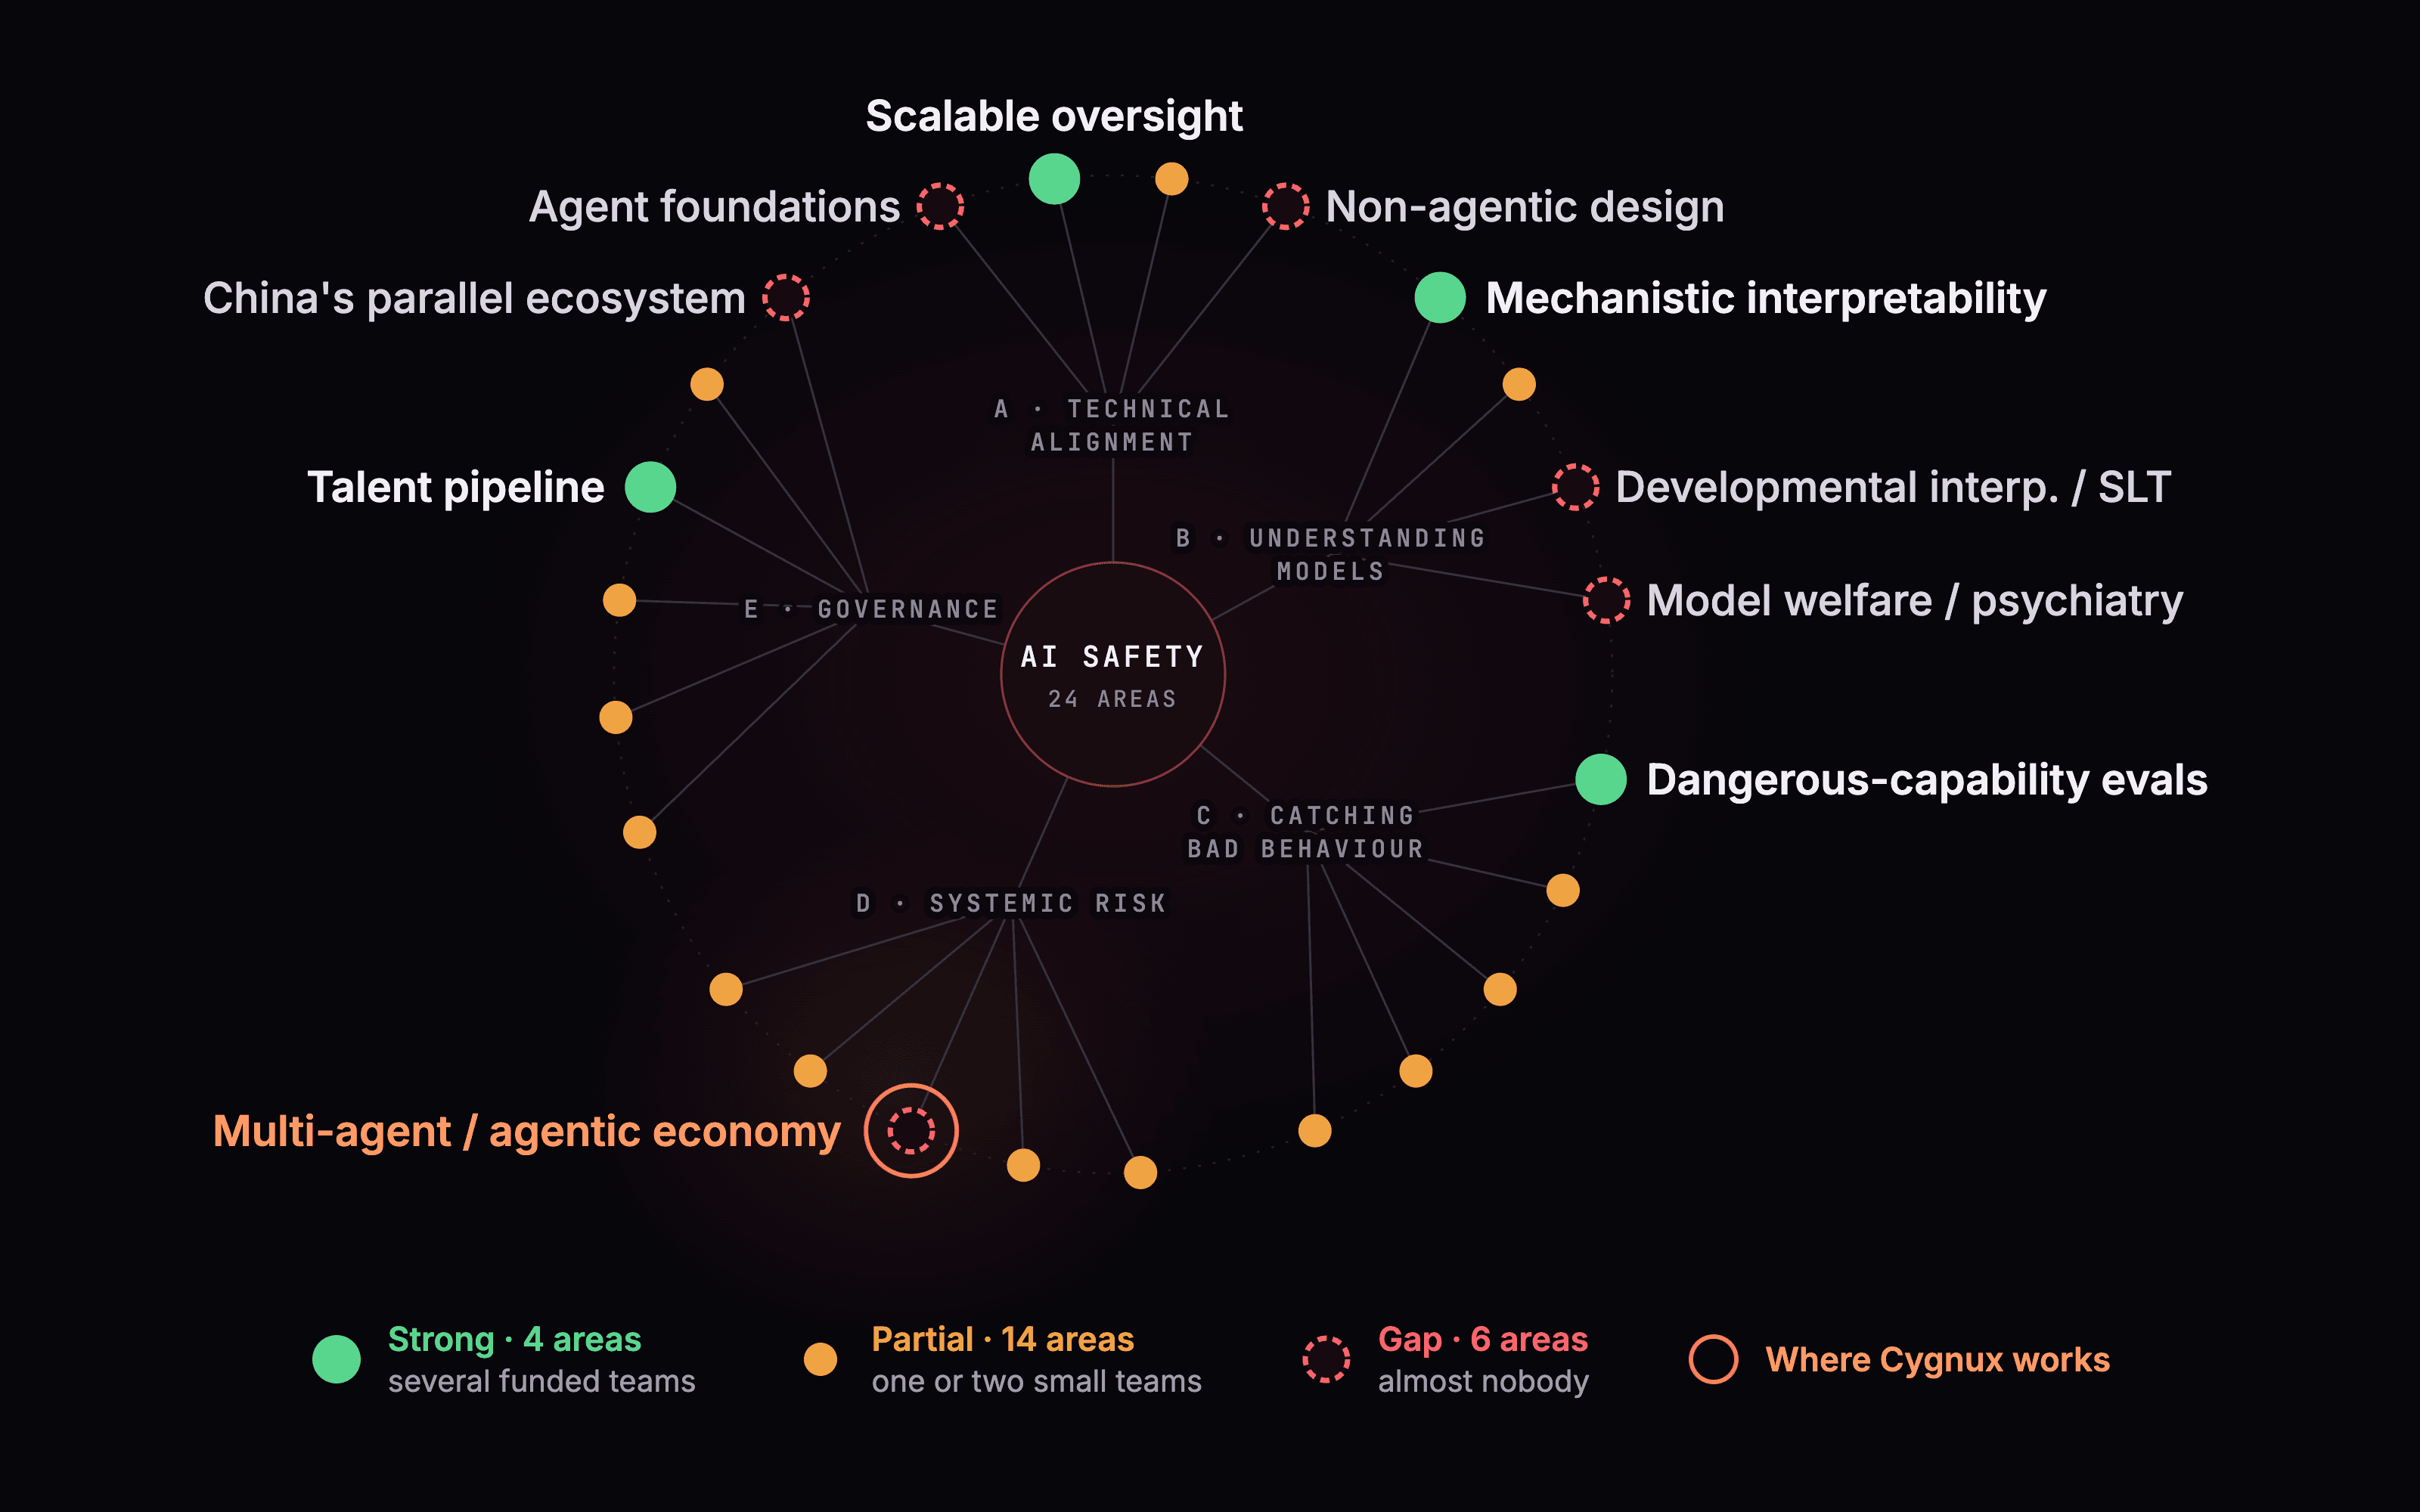
AI Safety Atlas

Published

A map of where AI safety effort goes, used to decide where the lab should work.

  • 24 areas across 5 clusters
  • Rated by how thickly each is covered
  • Multi-agent risk among the largest gaps
Field mapTaxonomyView →

Papers

Our published papers, in full, newest first. Each one explains the method, the results and what did not work.

Research paperProject: Proof-Carrying Messages

[Paper] PCM: A Proof-Carrying Message Protocol for Verifiable Multi-Agent Communication

When one AI agent tells another that “the tests passed” or “a person approved this refund”, the receiver has only the sender’s word.

Research paperProject: Tracekit Box

[Paper] Tracekit Box: Running AI Agents in Micro-VMs Where Every Way Out Is Decided and Signed

AI agents now do real jobs: they install packages, call model APIs with their operators’ keys, and change code in repositories that deploy to production.

Research paperProject: Tracekit

[Paper] Tracekit: Tamper-Evident Intent-Reasoning-Action Auditing for AI Agents

AI agents run shell commands, edit repositories, send email and move money with their operators’ credentials, and the record of what they did is usually a log that the agent, or whoever runs it, can edit.

Research paperProject: Proof-Gated Signing

[Paper] Proof-Gated Signing: Solver-Checked Transaction Guards that Hold Under State Drift for Onchain AI Agents

AI agents that control wallets read attacker-reachable content, so they can be steered into proposing harmful transactions.

Research paperProject: Frontier Lab

[Paper] Frontier Autolab: Organizational Memory, Adversarial Dissent and Temporal Leakage in Multi-Agent LLM Firms Across Fifty Years of Technological Change

Multi-agent LLM systems are increasingly structured like organizations, with roles, critics and shared memory, yet they are evaluated on tasks that last minutes.

Collaborate

Have a question one of these programs could answer?

We co-author studies with researchers and teams. Send the question you want answered, or see how we work with companies.